6 days ago
Under the Hood: Offensive Security
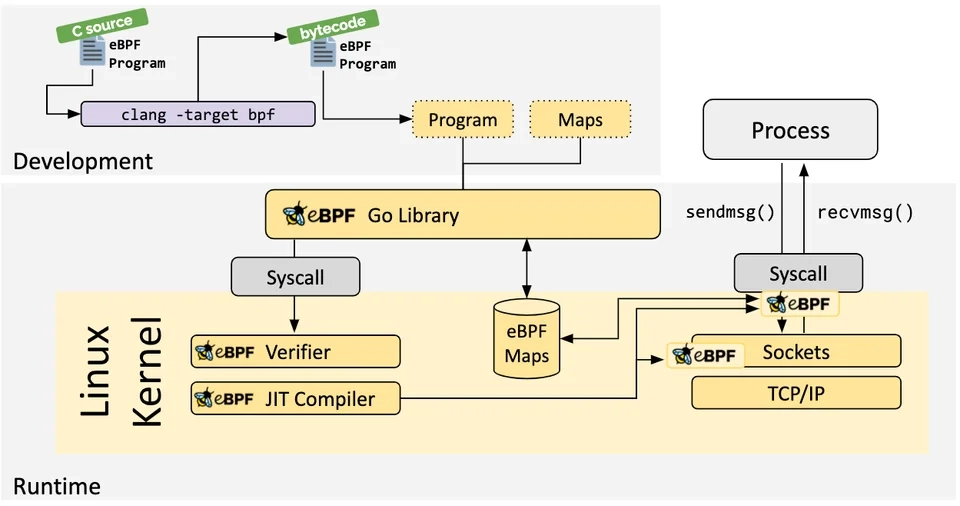
AegisSandbox was conceived to solve a critical blind spot in modern threat analysis: evasive malware routinely detects standard user-space hooks and debugging environments, concealing its true payload. Modern systems security is rarely won or lost at the user interface—it is determined deep within kernel space, container runtimes, and low-level API execution paths. While perimeter defense gets the headlines, true resilience requires understanding how attackers manipulate system calls and runtime boundaries to establish persistence. Designed to overcome these limitations, AegisSandbox is an ongoing project engineered to combine low-overhead eBPF kernel system-call interception with ChromaDB vector analytics and automated workspace emulation—delivering stealthy, real-time behavioral monitoring and AI-driven threat indexing directly from kernel space without tipping off the payload or compromising host performance.